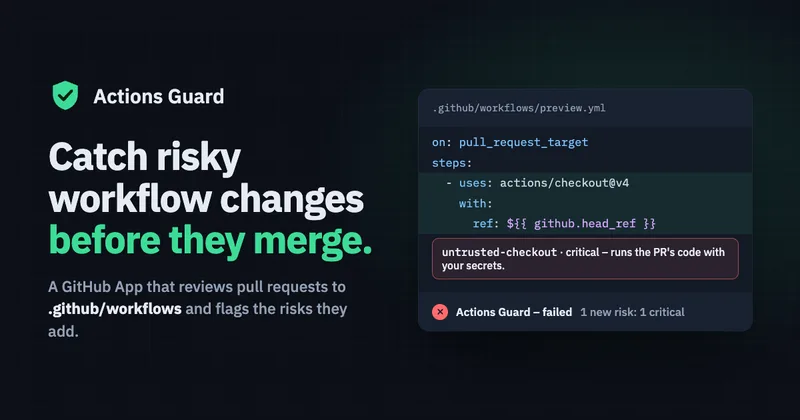
Catch risky workflow changes before they merge.
- Year
- 2026
- Role
- Author
- Stack
- TypeScript, GitHub Apps, YAML, Checks API
Overview
A GitHub App that reviews pull requests to .github/workflows and flags the security risks they add – script injection, untrusted checkouts, over-broad permissions.
Most supply-chain incidents on GitHub start with a workflow change nobody looked at closely: a `pull_request_target` that checks out the PR's code with secrets in scope, an expression interpolated straight into a shell, a token with write access it never needed.
Actions Guard reviews only the workflow diff of each pull request and reports the risks the change adds – as a check run with annotations on the exact lines, not a wall of pre-existing warnings.
Implementation
01
Diff-aware findings
Both versions of each workflow are analysed and only newly introduced risks are reported, so a review stays about the change at hand.
02
Annotations on the line
Findings map back to YAML source positions and land as check-run annotations right in the pull request.
Technical challenges
Precision over volume
Each rule targets a concrete exploit path – untrusted checkout with secrets, injection through `${{ }}` in `run:` – instead of style advice.